On September 30, 2026, Android reached a pivotal moment in its long history. Google officially initiated the first wave of its long-discussed sideloading restriction policy across select launch regions. For years, the open nature of Android meant downloading an .apk file from GitHub, F-Droid, or a web browser and installing it with a simple tap was second nature. Now, that foundational experience is undergoing its most aggressive overhaul to date.
The move stems from Google’s new mandatory Android Developer Verification Program, designed to curb malware and fraud by linking app distribution to verified real-world identities. However, the collateral damage lands directly on power users, open-source advocates, and popular modding ecosystems like Morphe and ReVanced.
As detailed in a comprehensive community breakdown on the r/MorpheApp subreddit, these new measures don’t completely kill sideloading—but they introduce distinct friction points that require users to adjust how they manage their devices.
What Is Changing and How the Restrictions Work
At the center of Google’s security overhaul is package name and signature key verification embedded within Google Play Services and Google Play Protect.
Under the new system, when you attempt to install an APK outside of officially recognized app stores, Android checks whether the app’s package name and signing key are registered with a verified developer in Google’s console. If the app is unregistered—or if it is a patched app using a altered signing key—the default package manager blocks the installation.
[ Unverified APK Attempt ]
           │
           ▼
[ Google Play Protect / GMS Check ] ──( Unregistered Signature )──► [ Installation Blocked ]
           │
           ▼
[ Bypass Pathways: ADB / Shizuku / Advanced Flow ] ──────────────► [ Successful Install ]
Who Is Affected?
Certified GMS Devices: Every Android phone running Google Mobile Services (Samsung, Xiaomi, OPPO, vivo, Motorola, Pixel, etc.) on Android 7 and above.
Geographic Rollout: The initial enforcement phase covers users in countries like Brazil, Indonesia, Singapore, and Thailand, according to Gadget Hacks’ detailed timeline analysis. Global rollout across all markets will proceed throughout 2027.
Who Is Excluded?
Non-GMS Operating Systems: Devices running HarmonyOS or open-source custom ROMs without Google Play Services (such as GrapheneOS) remain completely unaffected.
Rooted Devices: Users with full root privileges (Magisk, KernelSU, APatch) bypass the OS-level Play Protect package verifier altogether.
Why Patchers Like Morphe Are Hit Hardest
Apps designed to patch and modify existing software—such as Morphe, ReVanced, and standalone open-source utilities—rely on generating custom APKs locally on the user’s device. Because these patched binaries are re-signed using generic or newly generated signing keys, Google’s system classifies them as “unverified applications.”
While this mechanism is intended to stop bad actors from masquerading as legitimate banking or social media platforms, it simultaneously traps legitimate open-source utilities in the same net.
How to Bypass Android Sideloading Restrictions
Fortunately, Android has not become a completely closed ecosystem like iOS. Google left explicit pathways open for developers, power users, and enthusiasts. If your device has hit the first wave of restrictions, here are the four effective ways to maintain control over your phone.
Method 1: The “Advanced Flow” (Google’s Official Power-User Toggle)
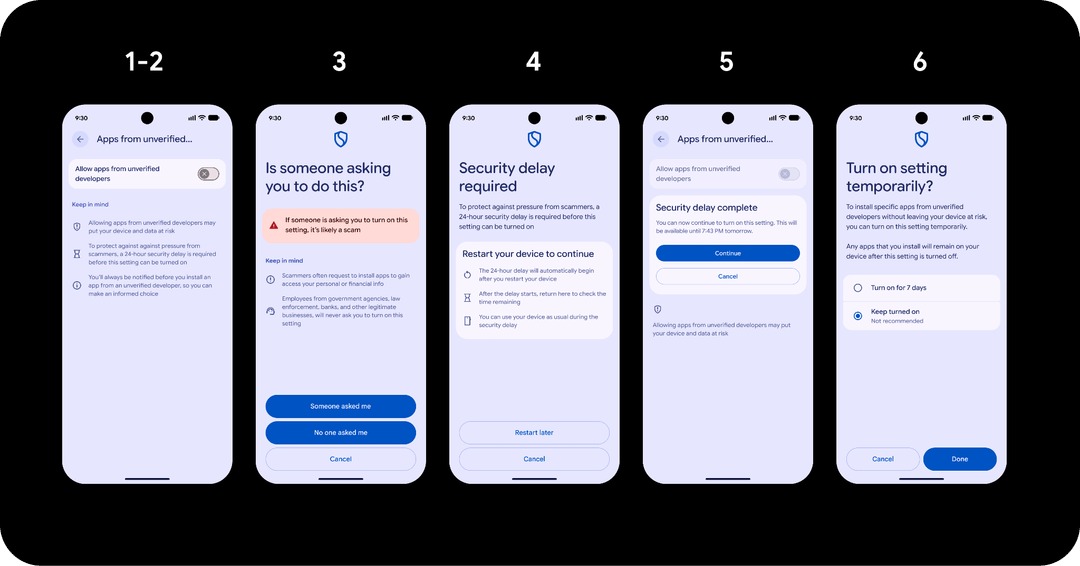
Google built a native pathway called “Advanced Flow” specifically for power users who want to install unverified apps without external software. However, it requires navigating a intentional 24-hour security delay.
Go to Settings > About Phone and tap Build Number seven times to enable Developer Options.
Navigate to Settings > System > Developer Options and locate Apps from Unverified Developers.
Toggle the switch ON, enter your PIN/Password, and confirm the warning dialog.
Restart your device.
Wait 24 hours. This cooling-off period is designed by Google to prevent social engineering attacks and malware installation scripts.
After 24 hours, return to the Apps from Unverified Developers setting and select Allow Indefinitely.
Crucial Tip for Banking Apps: Once you have completed the 24-hour verification and selected “Allow Indefinitely,” you can safely turn Developer Options OFF. Your permission to install unverified apps will remain active in the background, ensuring sensitive applications like mobile banking operate without flagging safety violations.
Method 2: Shizuku + Custom Installer (The Ideal Wireless Solution)
For most modders and Morphe users, using Shizuku paired with an installer utility (like InstallerX-Revived) is the smoothest solution.
Shizuku creates an on-device bridge using Android’s built-in Wireless Debugging framework. Because Wireless Debugging operates at the ADB (Android Debug Bridge) shell level, package installations executed through Shizuku bypass Google Play Protect’s unverified app block entirely—no 24-hour waiting period required, and no PC needed.
Method 3: ADB (Android Debug Bridge via PC)
If you have a computer handy, installing apps using classic ADB commands remains completely unrestricted.
Connecting your phone via USB debugging and issuing standard commands like adb install package.apk routes the installation directly through system-level developer channels, bypassing the user-facing package installer restriction completely.
Method 4: System App Placeholder Strategy
Google introduced a system-level application named Android Developer Verifier to enforce verification checks. Some community members have developed “placeholder” packages that assign high version numbers to this system app to prevent it from auto-updating. While effective for specific build configurations, leveraging Shizuku or Advanced Flow remains a cleaner, more sustainable long-term option.
Bypassing Methods Compared
| Method | Setup Time | Requires PC? | 24-Hour Wait? | Banking App Friendly? |
| Advanced Flow | 5 mins (+24h wait) | No | Yes | Yes (if Developer Options turned off after) |
| Shizuku + Installer | 3 mins | No | No | Yes |
| ADB Command Line | 2 mins | Yes | No | Yes |
| Root Access | Complex | Yes (One-time) | No | Requires Root Hiding |
Security vs. Freedom: The Bigger Picture
Google’s stance is straightforward: cybercrime and side-loaded phishing apps are growing threats, and requiring verified identity credentials makes it significantly harder for malicious actors to operate anonymously.
Yet, for many long-time Android users, the ability to freely compile, modify, and install software without corporate pre-approval is the exact reason they chose Android over competitors. As the policy expands globally toward its 2027 target, understanding tools like ADB and Shizuku will no longer be niche knowledge—it will be essential survival gear for maintaining true ownership of your hardware.